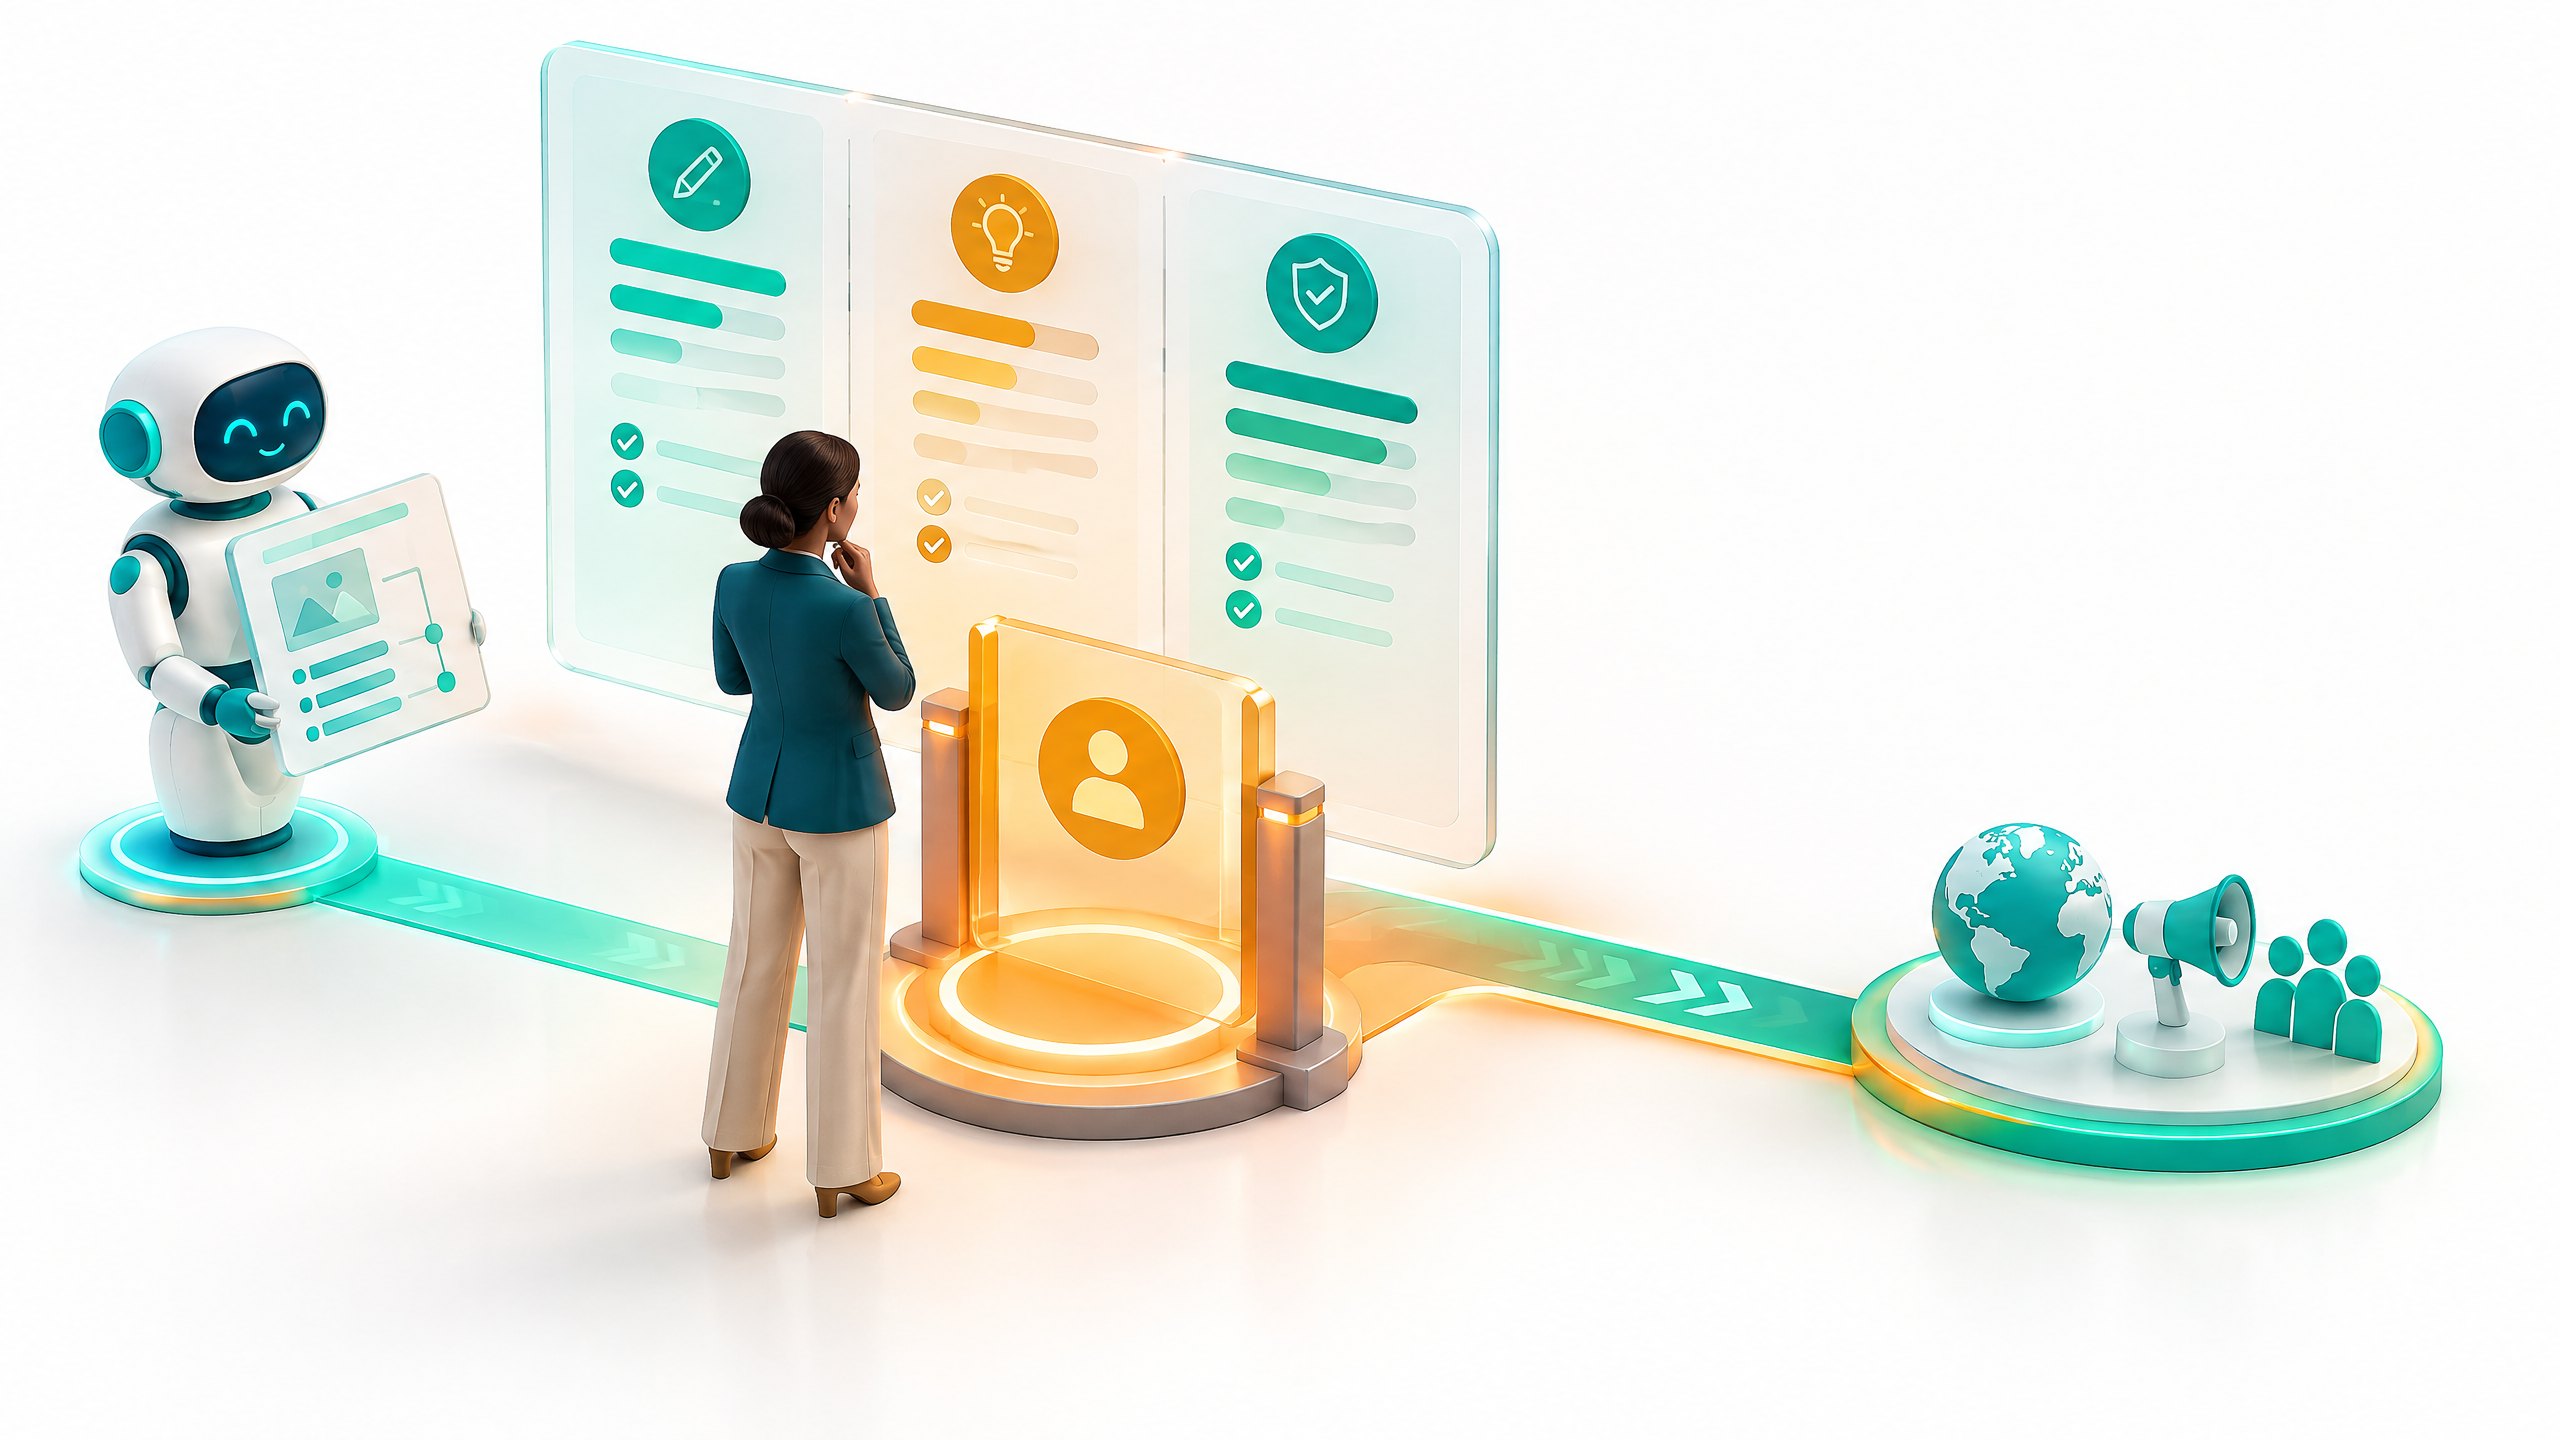
The short answer
AI agents need an operational identity that looks more like an employee record than an anonymous background automation: a unique identifier, a named business owner, a defined role, scoped access, action evidence and a way to revoke the access. They do not need employee-style blanket permissions, a shared human login or the ability to act as if they were legally independent people.
Microsoft’s 2026 Digital Defense Report makes the security basis explicit. Microsoft says that as AI agents enter the enterprise, security controls need to extend to their identities, permissions, data and tools. Its accompanying security post says the report examines agent identity, appropriate access, authentication between agents, attribution and the ability to revoke access. Those are useful implementation topics, not a claim that Microsoft has created a universal agent-ID standard.
Modi’s view: Think of an enterprise agent as a controlled operational identity, not a digital colleague with everyone else’s permissions. Give it a job description, a manager, an access card with limited rooms, a work log and a way to deactivate that card. Do not hand it the master key because the demo looked impressive.
Why identity is now part of AI security
Traditional software security already depends on knowing what is acting in an environment. A person has a user identity. A service has a service account or workload identity. A device has a managed record. Each can be authenticated, granted a limited role, monitored and disabled.
AI agents complicate that model because they may use several tools, make decisions across several steps and run for longer than a single chat interaction. They can retrieve information, call an API, update a record, draft a message, trigger another workflow and request more access. If all of that appears in logs only as “automation” or under a staff member’s account, an organization cannot easily answer who acted, why it was allowed or how to stop just that agent.
Microsoft’s report places this in a wider threat context. It says a controlled evaluation chained 32 stages together and that the median time from vulnerability discovery in the wild to weaponization has fallen to well below 24 hours, while enterprise remediation of critical external vulnerabilities can take 30 to 60 days. These are Microsoft’s reported findings about the threat landscape, not a prediction that a business agent will run an autonomous attack. The practical implication is that access decisions and detection need to be faster, clearer and more continuous than a quarterly permissions review.
Employee-style identity does not mean employee status
The employee analogy is useful only as an operating metaphor. An AI agent is not a legal employee, an accountable director or a person capable of accepting a customer obligation. The organization deploying it remains responsible for the controls around the workflow.
The analogy helps because a sensible employment record contains details an agent deployment also needs:
| Employee-style record element | Agent equivalent | Why it matters |
|---|---|---|
| Worker ID | Unique agent or workload identifier | Enables attribution in logs and connected systems |
| Manager | Named business owner | Creates a route for policy, exception and performance decisions |
| Job description | Bounded workflow purpose | Stops an assistant from becoming an undefined general-access account |
| Access card | Scoped credentials and approved tools | Limits the systems and data it can reach |
| Training and review | Test evidence, change review and periodic access recertification | Verifies the agent still performs the permitted job safely |
| Offboarding | Credential disablement, token rotation and workflow shutdown | Makes revocation possible when a role, vendor or risk changes |
The missed step is often the role definition. Teams buy an “AI agent” and connect it to a mailbox, CRM, knowledge base, analytics dashboard and browser without writing down the exact business job. That creates a broad identity with unclear authority. A cleaner design starts with one job: for example, “prepare a source-linked weekly account update from designated datasets” rather than “assist the revenue team.”
The minimum viable agent identity record
A robust identity system can be complex. A useful first deployment does not need to be. It needs a record that commercial, security and operations owners can inspect.
1. Stable identity and environment
Give the agent a unique, non-human identifier and keep production separate from testing. The identity should appear in access logs, tool events and workflow records. Do not use a senior employee’s profile as the agent’s permanent identity simply because it was easy during setup.
2. Named business and technical owners
One person or team should own the commercial outcome; another can own the technical configuration. The same individual may fulfill both roles in a small team, but the distinction prevents an agent from becoming ownerless when a prompt author changes jobs or a vendor relationship ends.
3. Purpose and approved task class
Write the intended task in a way that supports a decision. “Read approved research sources and produce a cited brief” is measurable. “Grow pipeline” is not. If the agent begins serving a new purpose, treat that as a change that needs review rather than silently extending its reach.
4. Data boundary and tools
List the sources it may use and the data it must not access. List the APIs, plugins or browser actions that are allowed. Microsoft’s security guidance emphasizes that AI security depends not only on the model but on reachable data, tools, identities, permissions and surrounding infrastructure. This is why an excellent prompt cannot compensate for an over-privileged integration.
5. Authority and approval threshold
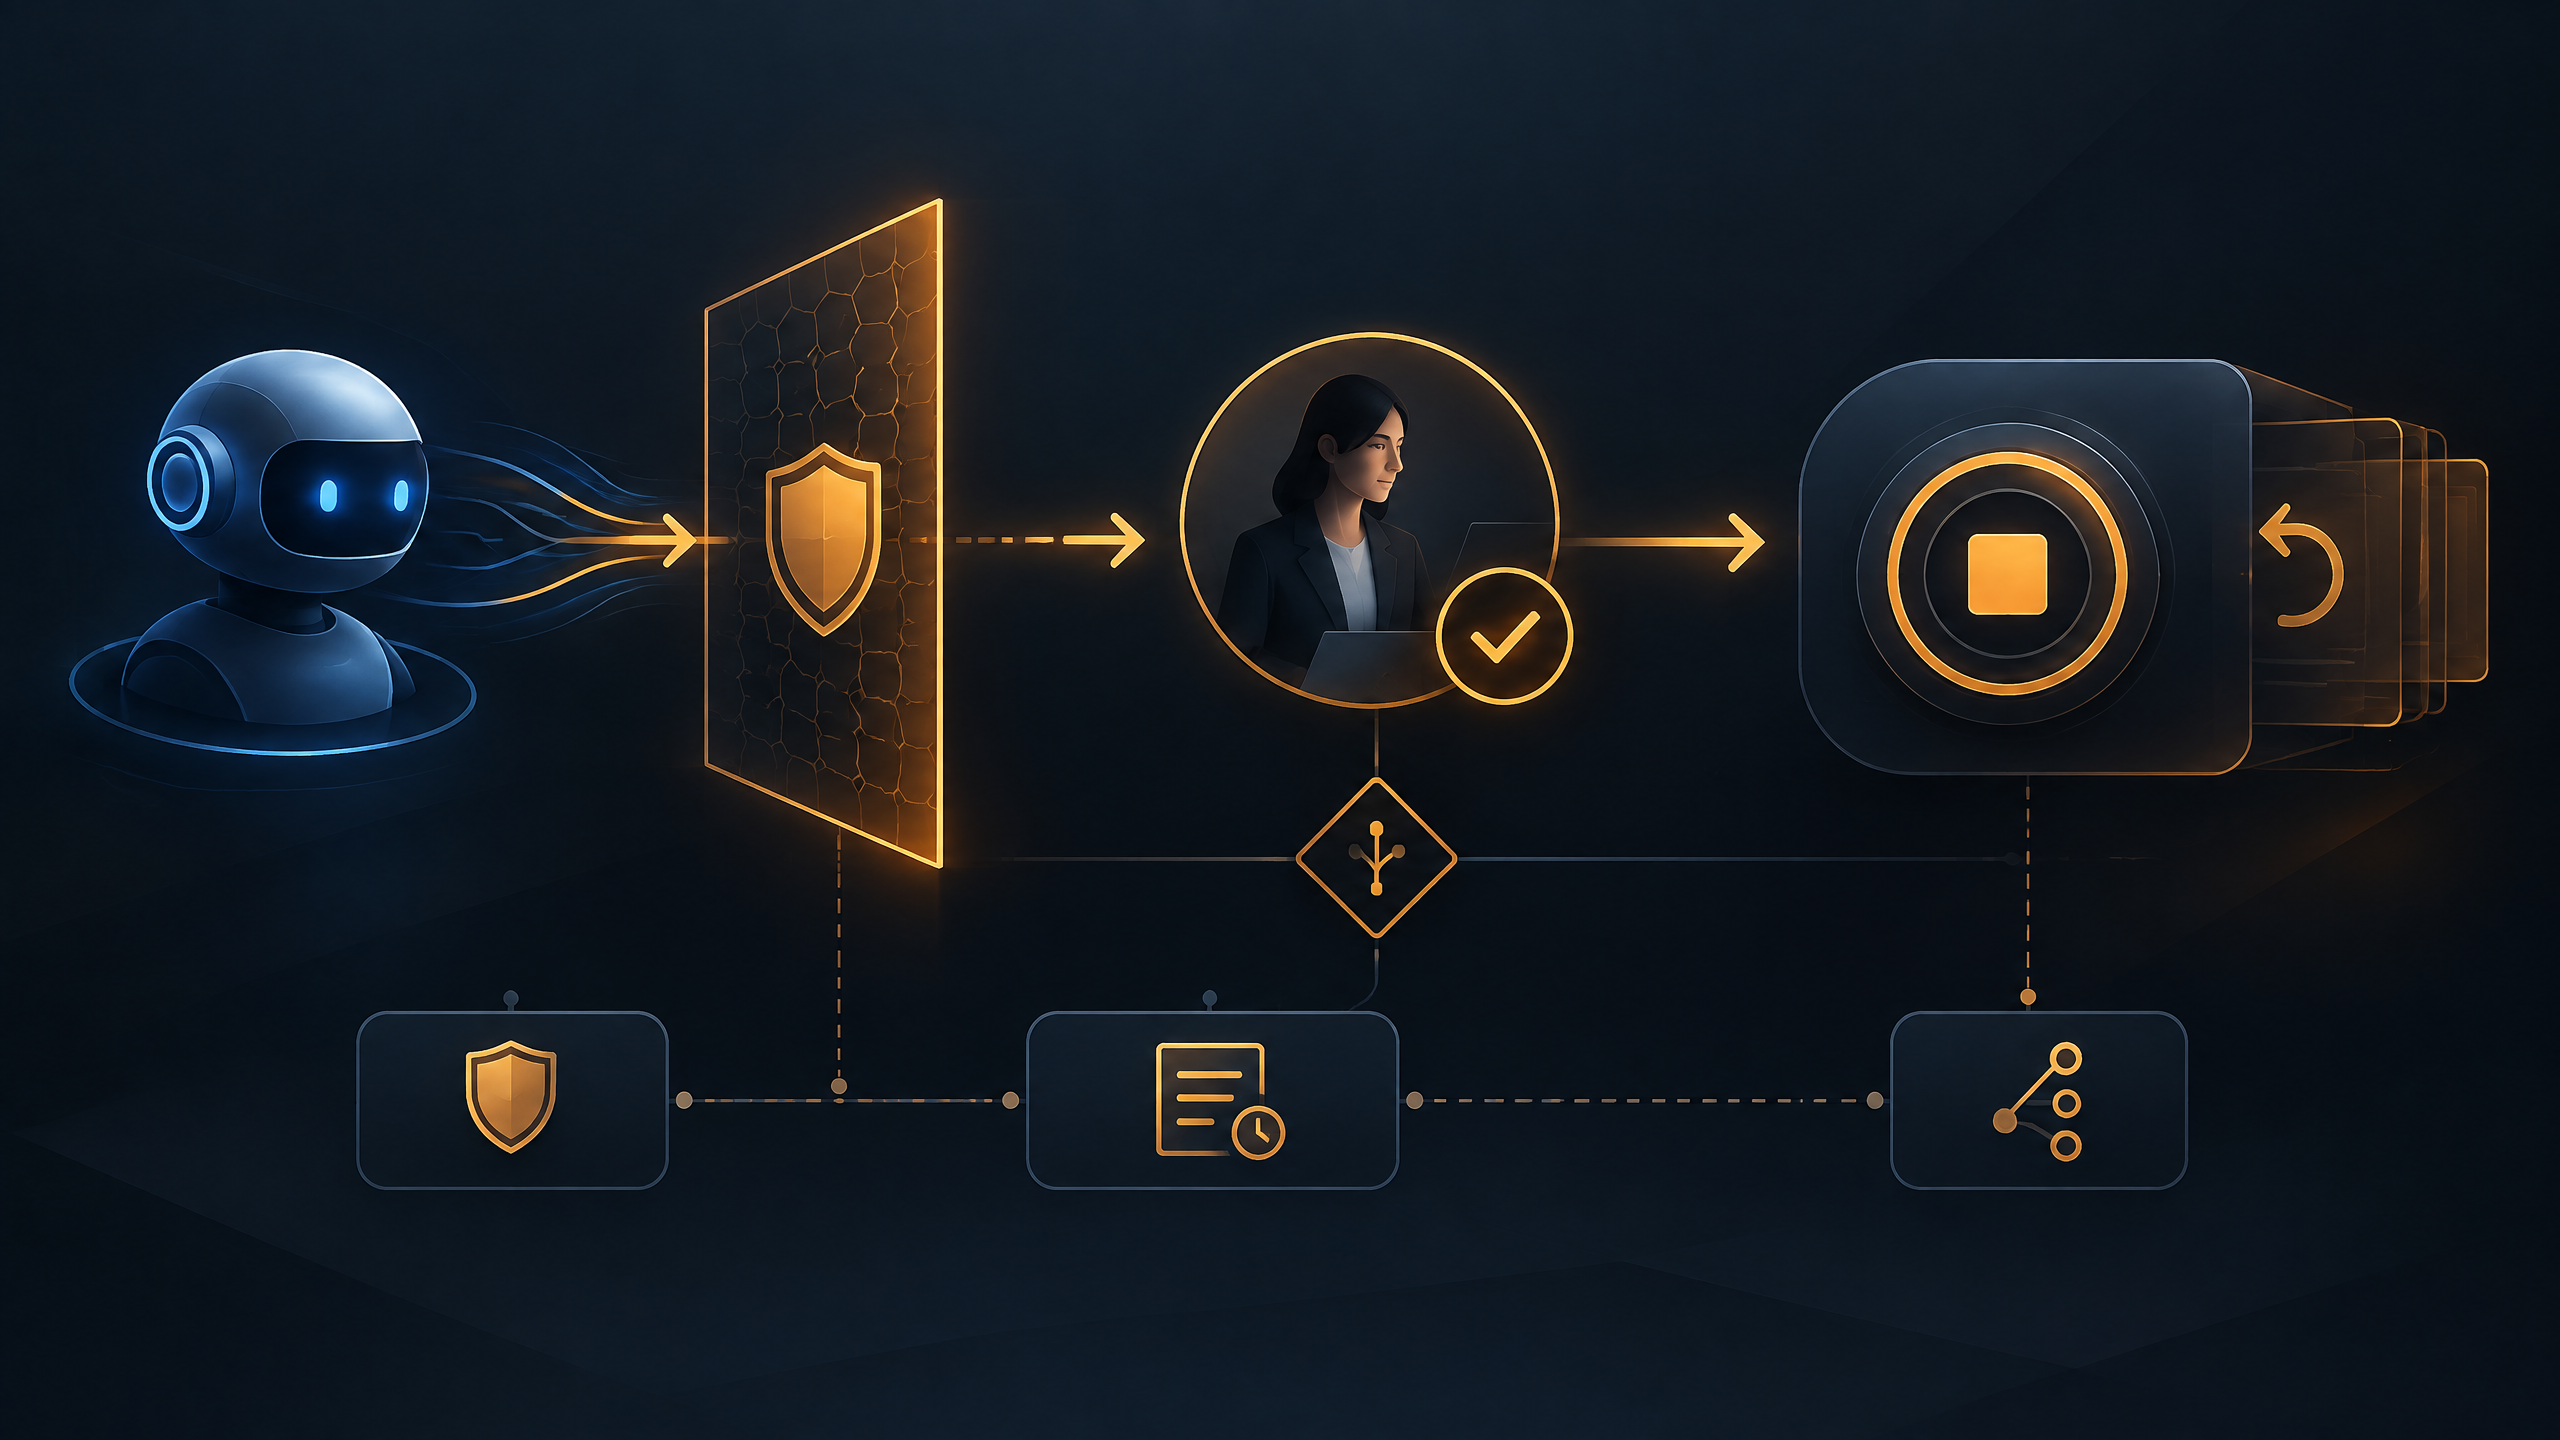
Specify whether the agent can read, propose, change or commit. The Maximum Autonomous Consequence framework adds a useful question: what is the highest-consequence action possible before a person must intervene? If that answer is unclear, the permission set is too broad.
6. Evidence and monitoring
Retain a practical record of important instructions, source context, tool actions, output, approval and exception. The goal is not to record every token forever. It is to preserve enough context to investigate a material action, explain an unusual recommendation and improve a recurring workflow.
7. Expiry, review and revocation
Every agent should have a review date. Access can become inappropriate because a vendor changes, a workflow expands, an employee moves roles or a data category changes. Test how access is disabled and how the system recovers. Revocation is not just deleting a chat history; it may mean disabling the workload identity, removing API keys, ending scheduled jobs and rotating secrets.
Least privilege is the commercial unlock, not the constraint
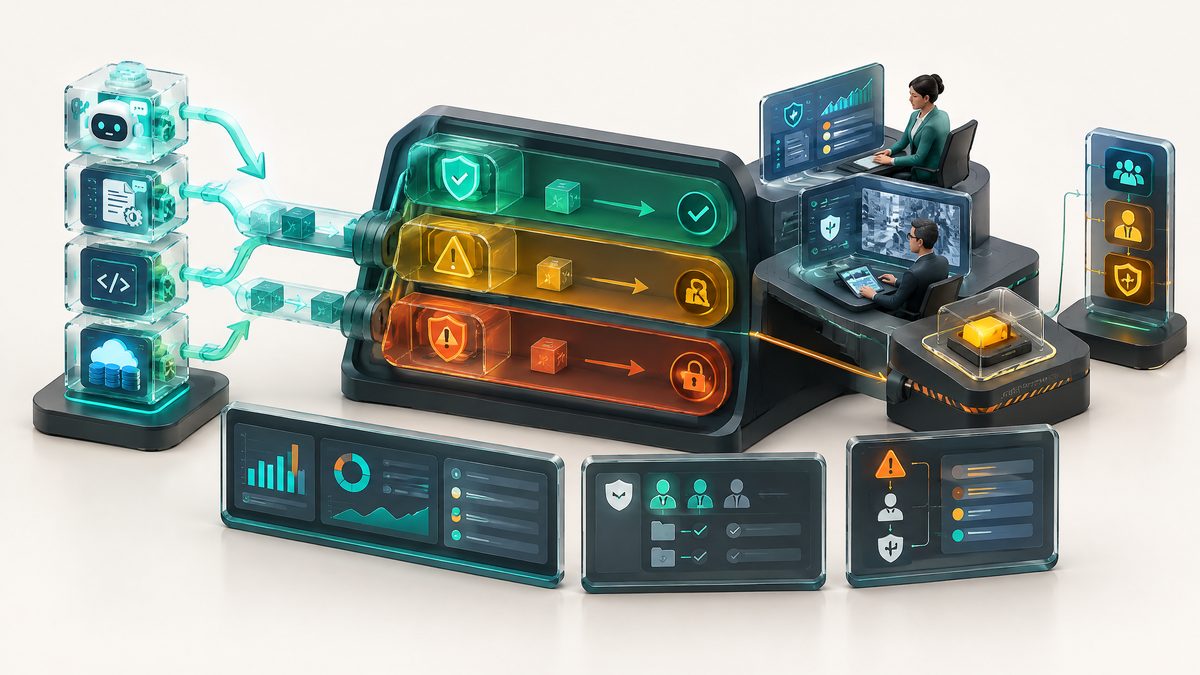
Least privilege is often described as a security tax. For agents, it can make adoption easier. A commercial leader is more likely to approve a workflow when it can be explained as: “this agent can read these approved sources, draft these reports and write only to this review queue.”
That is a more credible operating design than “the agent needs broad access because it is supposed to be helpful.” It also creates a clearer test. The team can measure whether the bounded workflow saves time, improves evidence quality or reduces a particular backlog. If it does, access can be extended deliberately. If it fails, the blast radius is smaller.
A typical marketing and sales pattern looks like this:
| Workflow | Minimum useful access | Action that remains human-owned |
|---|---|---|
| Account research | Public sources and approved internal reference library | Creating a prospect record or making a commercial claim |
| Content QA | Published content, editorial policy and approved sources | Publishing a material change or a high-risk statement |
| Campaign analysis | Read-only performance data and defined metrics | Changing budgets, targeting or conversion definitions |
| Lead triage | Defined intake fields and approved routing rules | Rejecting a qualified lead, changing opportunity value or contacting a sensitive record |
| Customer service preparation | Relevant case record and approved policy articles | Financial compensation, exception handling or regulated advice |
The purpose is not to limit value. It is to ensure that value survives review by security, legal, operations and the customer-facing team.
Avoid the “shadow agent” problem
Shadow IT was manageable when it meant a spreadsheet or unsanctioned SaaS subscription. A shadow agent can combine data access, memory, external tools and delegated actions. It may be introduced through a browser extension, a vendor integration, a departmental pilot or an individual employee’s account.
Begin with discovery. Ask teams what assistants, automations and AI-enabled tools are already connected to mailboxes, calendars, CRM, analytics, code repositories, customer-support systems and advertising platforms. Do not frame this as a punitive audit. The aim is to understand the real operating environment before an incident or data request does it for you.
Then classify agents by consequence, not buzzword. A source-summarization assistant is different from a browser agent with customer-data access. A workflow that drafts a message is different from a workflow that sends it. This helps leaders focus controls on the system paths that could create the most harm or the hardest recovery.
Microsoft’s identity and access emphasis fits this approach, as do the controls discussed in our analysis of the OpenAI multi-agent incident and agent liability in commerce. The common lesson is not “avoid agents.” It is “know which identity did what, under which scope, and how to remove it.”
A 30-day agent identity program
Days 1–5: discover agents and service identities. Inventory AI-enabled workflows that access business systems. Include vendor agents, custom scripts, extensions and scheduled automations.
Days 6–10: assign owners and purposes. Give each material workflow a business owner, a technical owner and a one-sentence scope.
Days 11–15: reduce shared credentials. Replace shared human logins where feasible with separate identities. Remove broad permissions that are not required for the defined task.
Days 16–22: define the authority map. State what each agent can read, propose, change and commit to. Identify the approval and stop conditions.
Days 23–30: test evidence and revocation. Select one live workflow. Confirm that a reviewer can locate its recent actions, disable its access and recover or escalate an unexpected case.
For teams building this into a broader go-to-market operating model, AI governance and agentic AI workflow design are complementary: one sets the decision boundaries; the other makes the bounded workflow useful.
For leadership reading, Responsible AI: Implement an Ethical Approach in your Organization is an optional Amazon UK Associates resource. It is not evidence of security, compliance, legal status or suitability for any particular agent or vendor. Integrated.Social may earn from qualifying purchases.
The bottom line
As agents become more persistent and connected, the enterprise needs more than a prompt library and a list of vendors. It needs a secure operational identity for each material agent, a named owner, limited access, action evidence and a tested way to revoke the permission. Give an agent a controlled ID, not an employee’s master key.
References
- Microsoft: Insights from the 2026 Microsoft Digital Defense Report, 1 October 2026.
- Microsoft: 2026 Digital Defense Report, 1 October 2026.
- NIST: AI Risk Management Framework.
About the Author
Modi Elnadi is the founder of Integrated.Social, a London AI growth consultancy working across B2B, B2C, B2B2C and DTC. Since 2014, he has helped commercial teams connect performance marketing, AI-search visibility and governed AI workflows to clear evidence and accountable outcomes. His view: delegation earns trust only when its identity, authority, evidence and human escalation path are visible. Connect with Modi on LinkedIn or explore AI governance.