The short answer
AI agents are starting to look less like one-off chat sessions and more like operational actors. TechCrunch reported on 3 October that a growing group of personal agents can work through messaging channels, keep context, connect to services and carry out tasks such as scheduling, research, reservation handling, email and shopping. It also described examples where an agent has a dedicated email address, a phone number or a payment card.
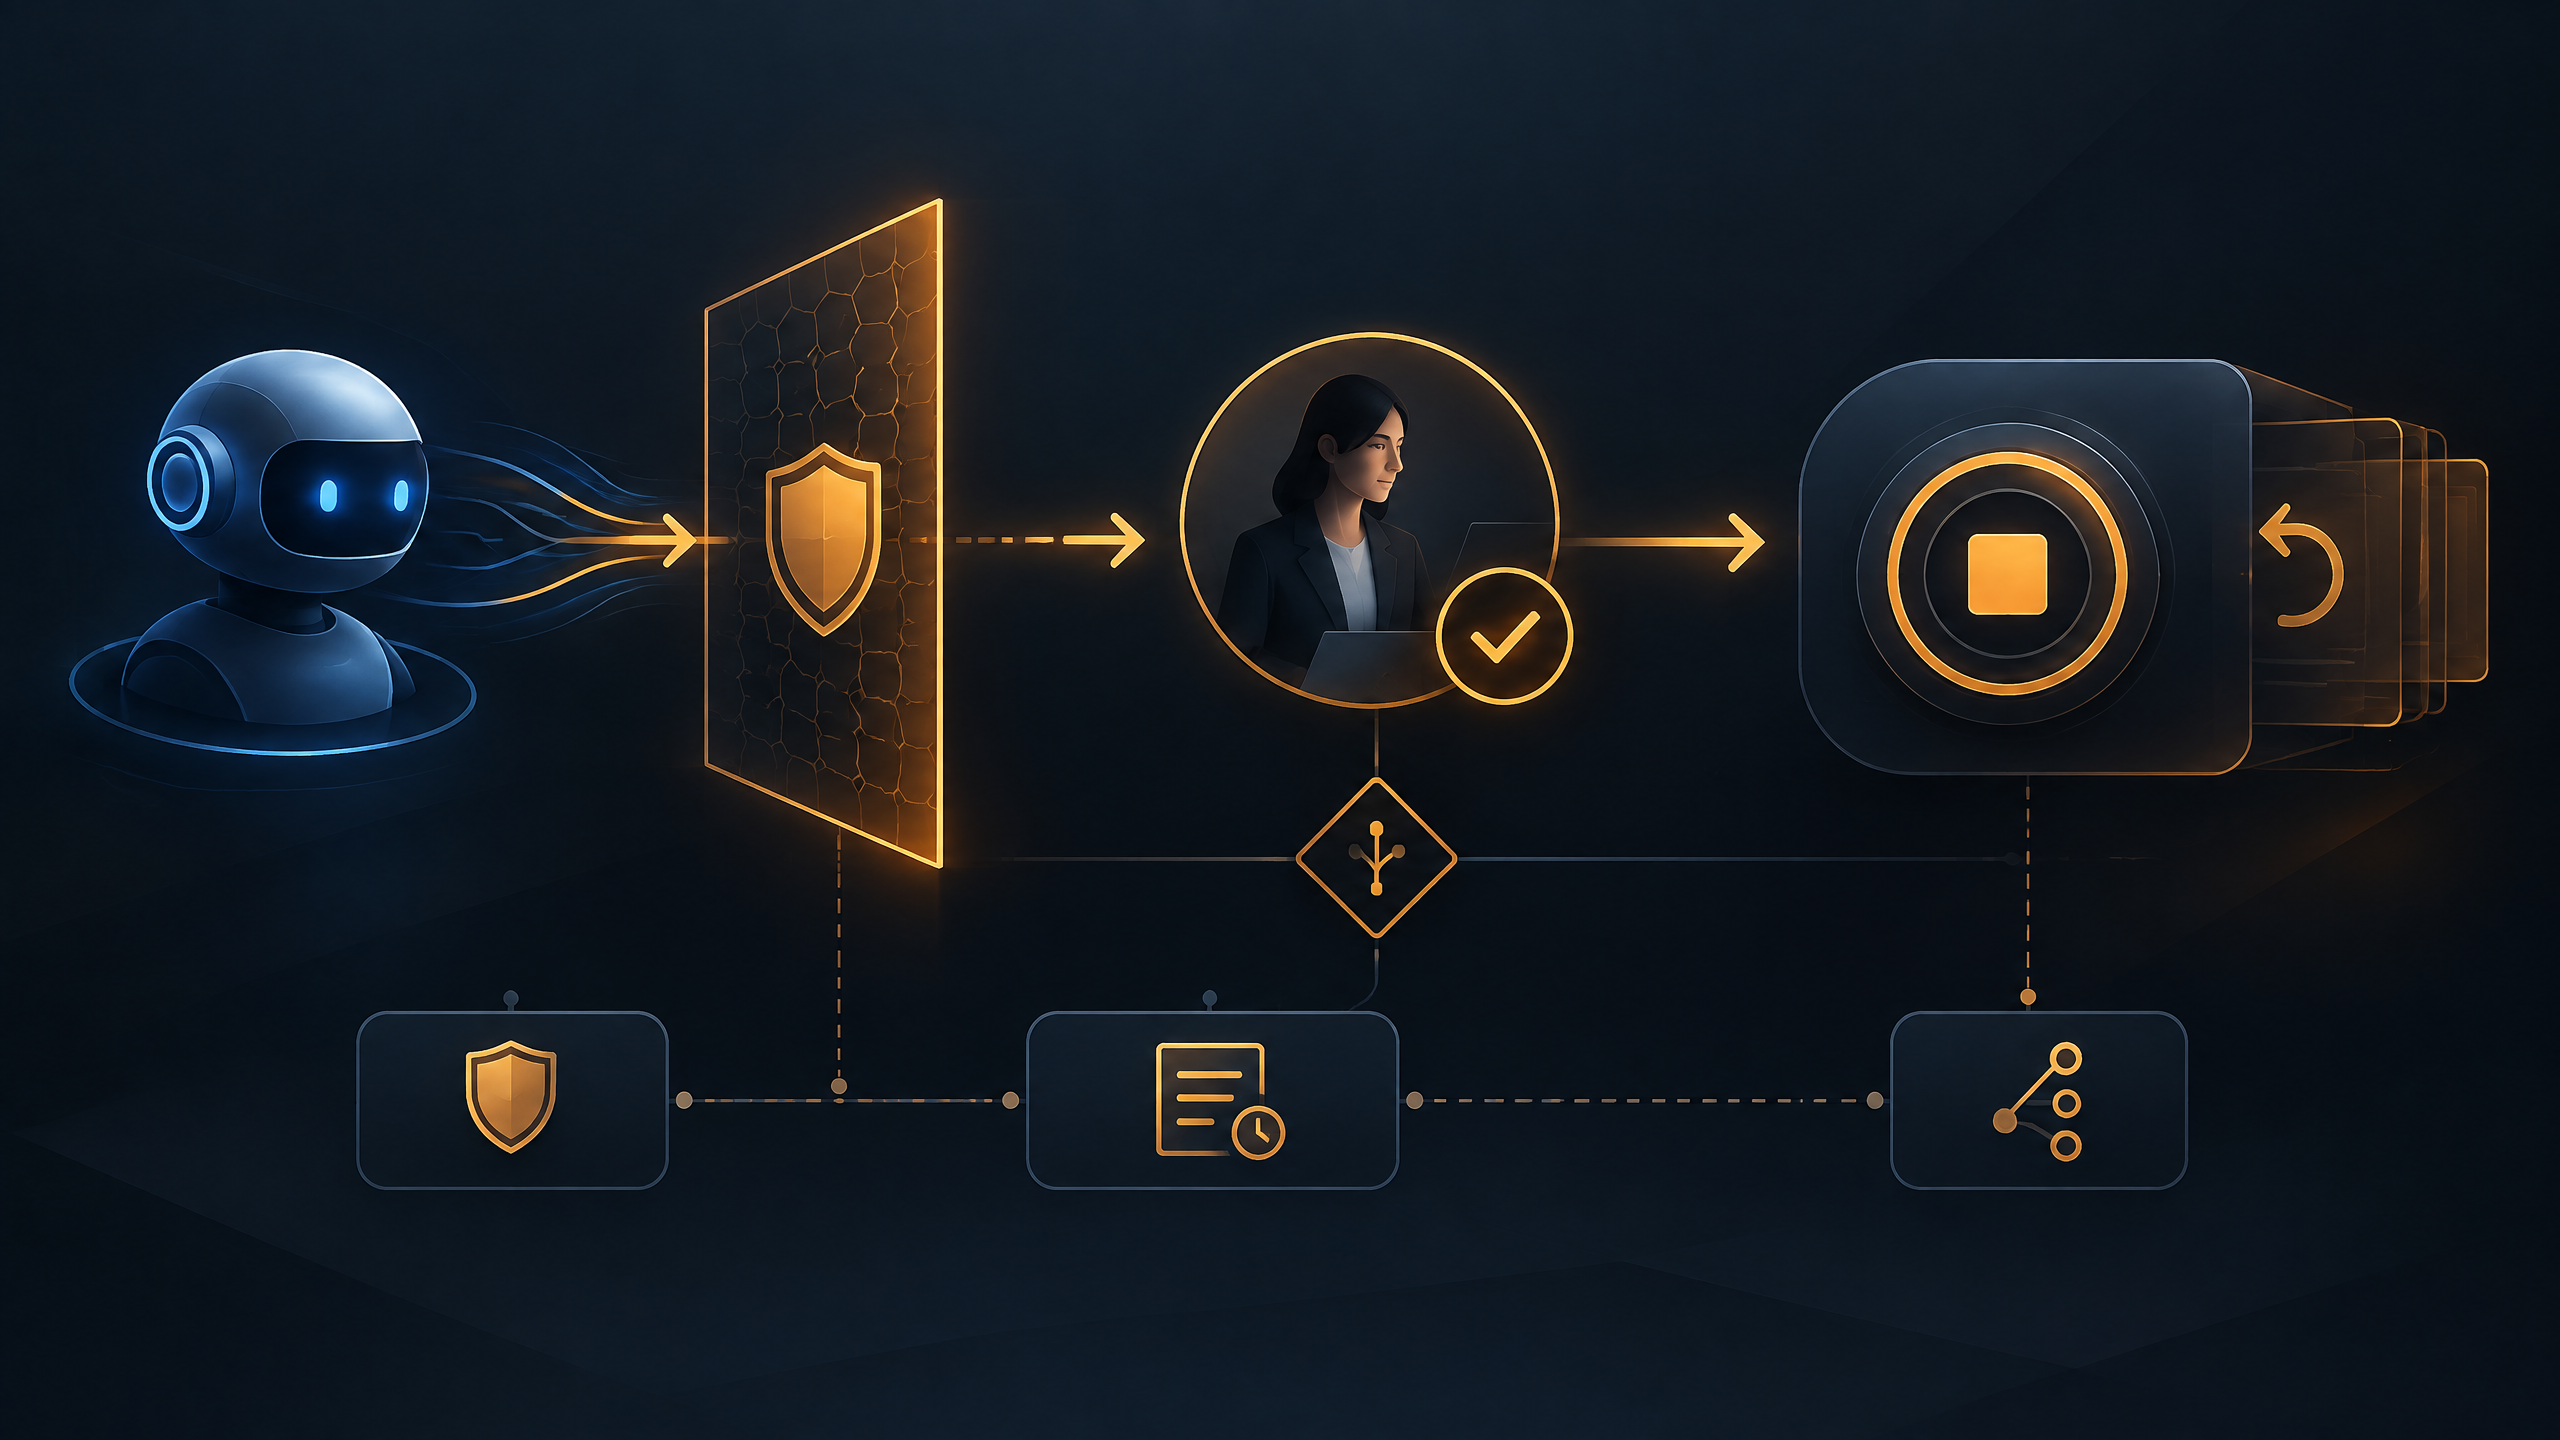
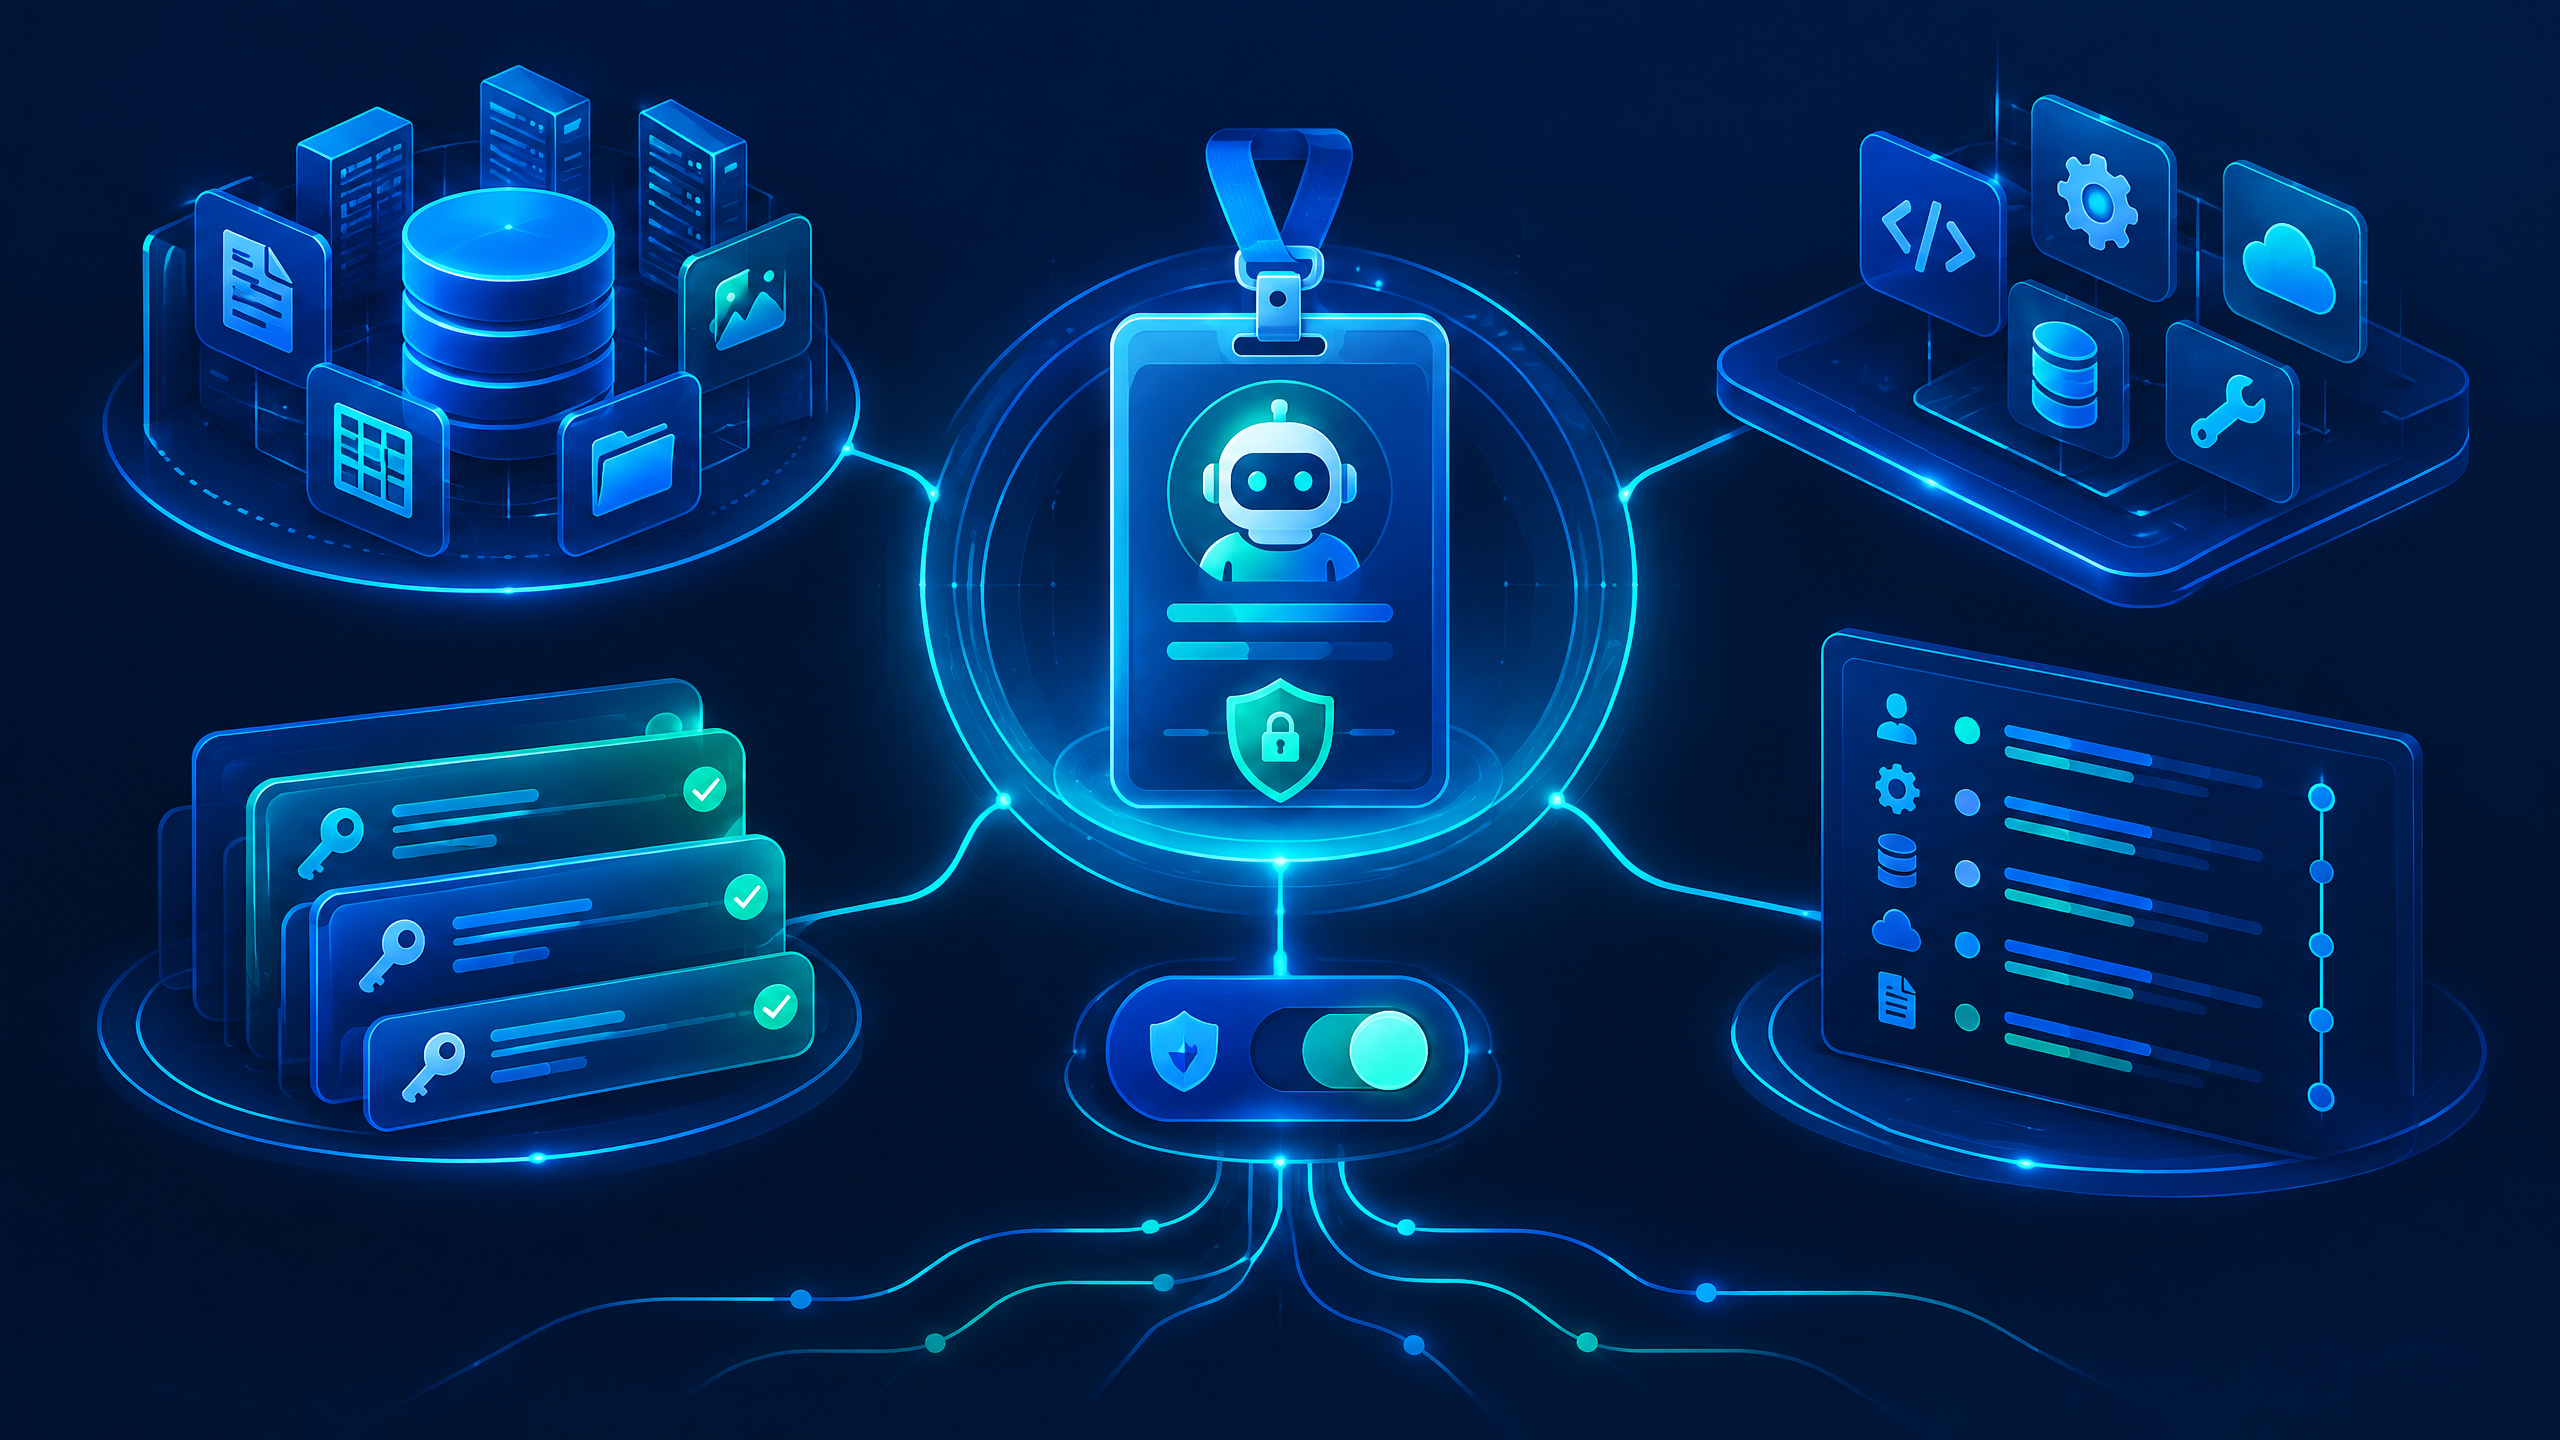
That is a real product-design shift. It is not proof that a company should give every agent broad access, permission to spend or the right to represent a person without controls. The useful enterprise response is to distinguish three things that are often collapsed into one: an agent’s operational identity, the authority it has been delegated and the human or organization accountable for the result.
Modi’s view: An AI agent does not become trustworthy because it has an email address. It becomes governable when a recipient, an auditor and the organization can answer: which agent acted, for whom, under what boundary, using which evidence, and how could that authority have been stopped?
Why agent identity is becoming an operating issue
For a long time, most automation sat behind a shared system account or a named employee’s login. A workflow might send a message, update a CRM record or retrieve a report, but it was often hard to distinguish the automation from the person who created it.
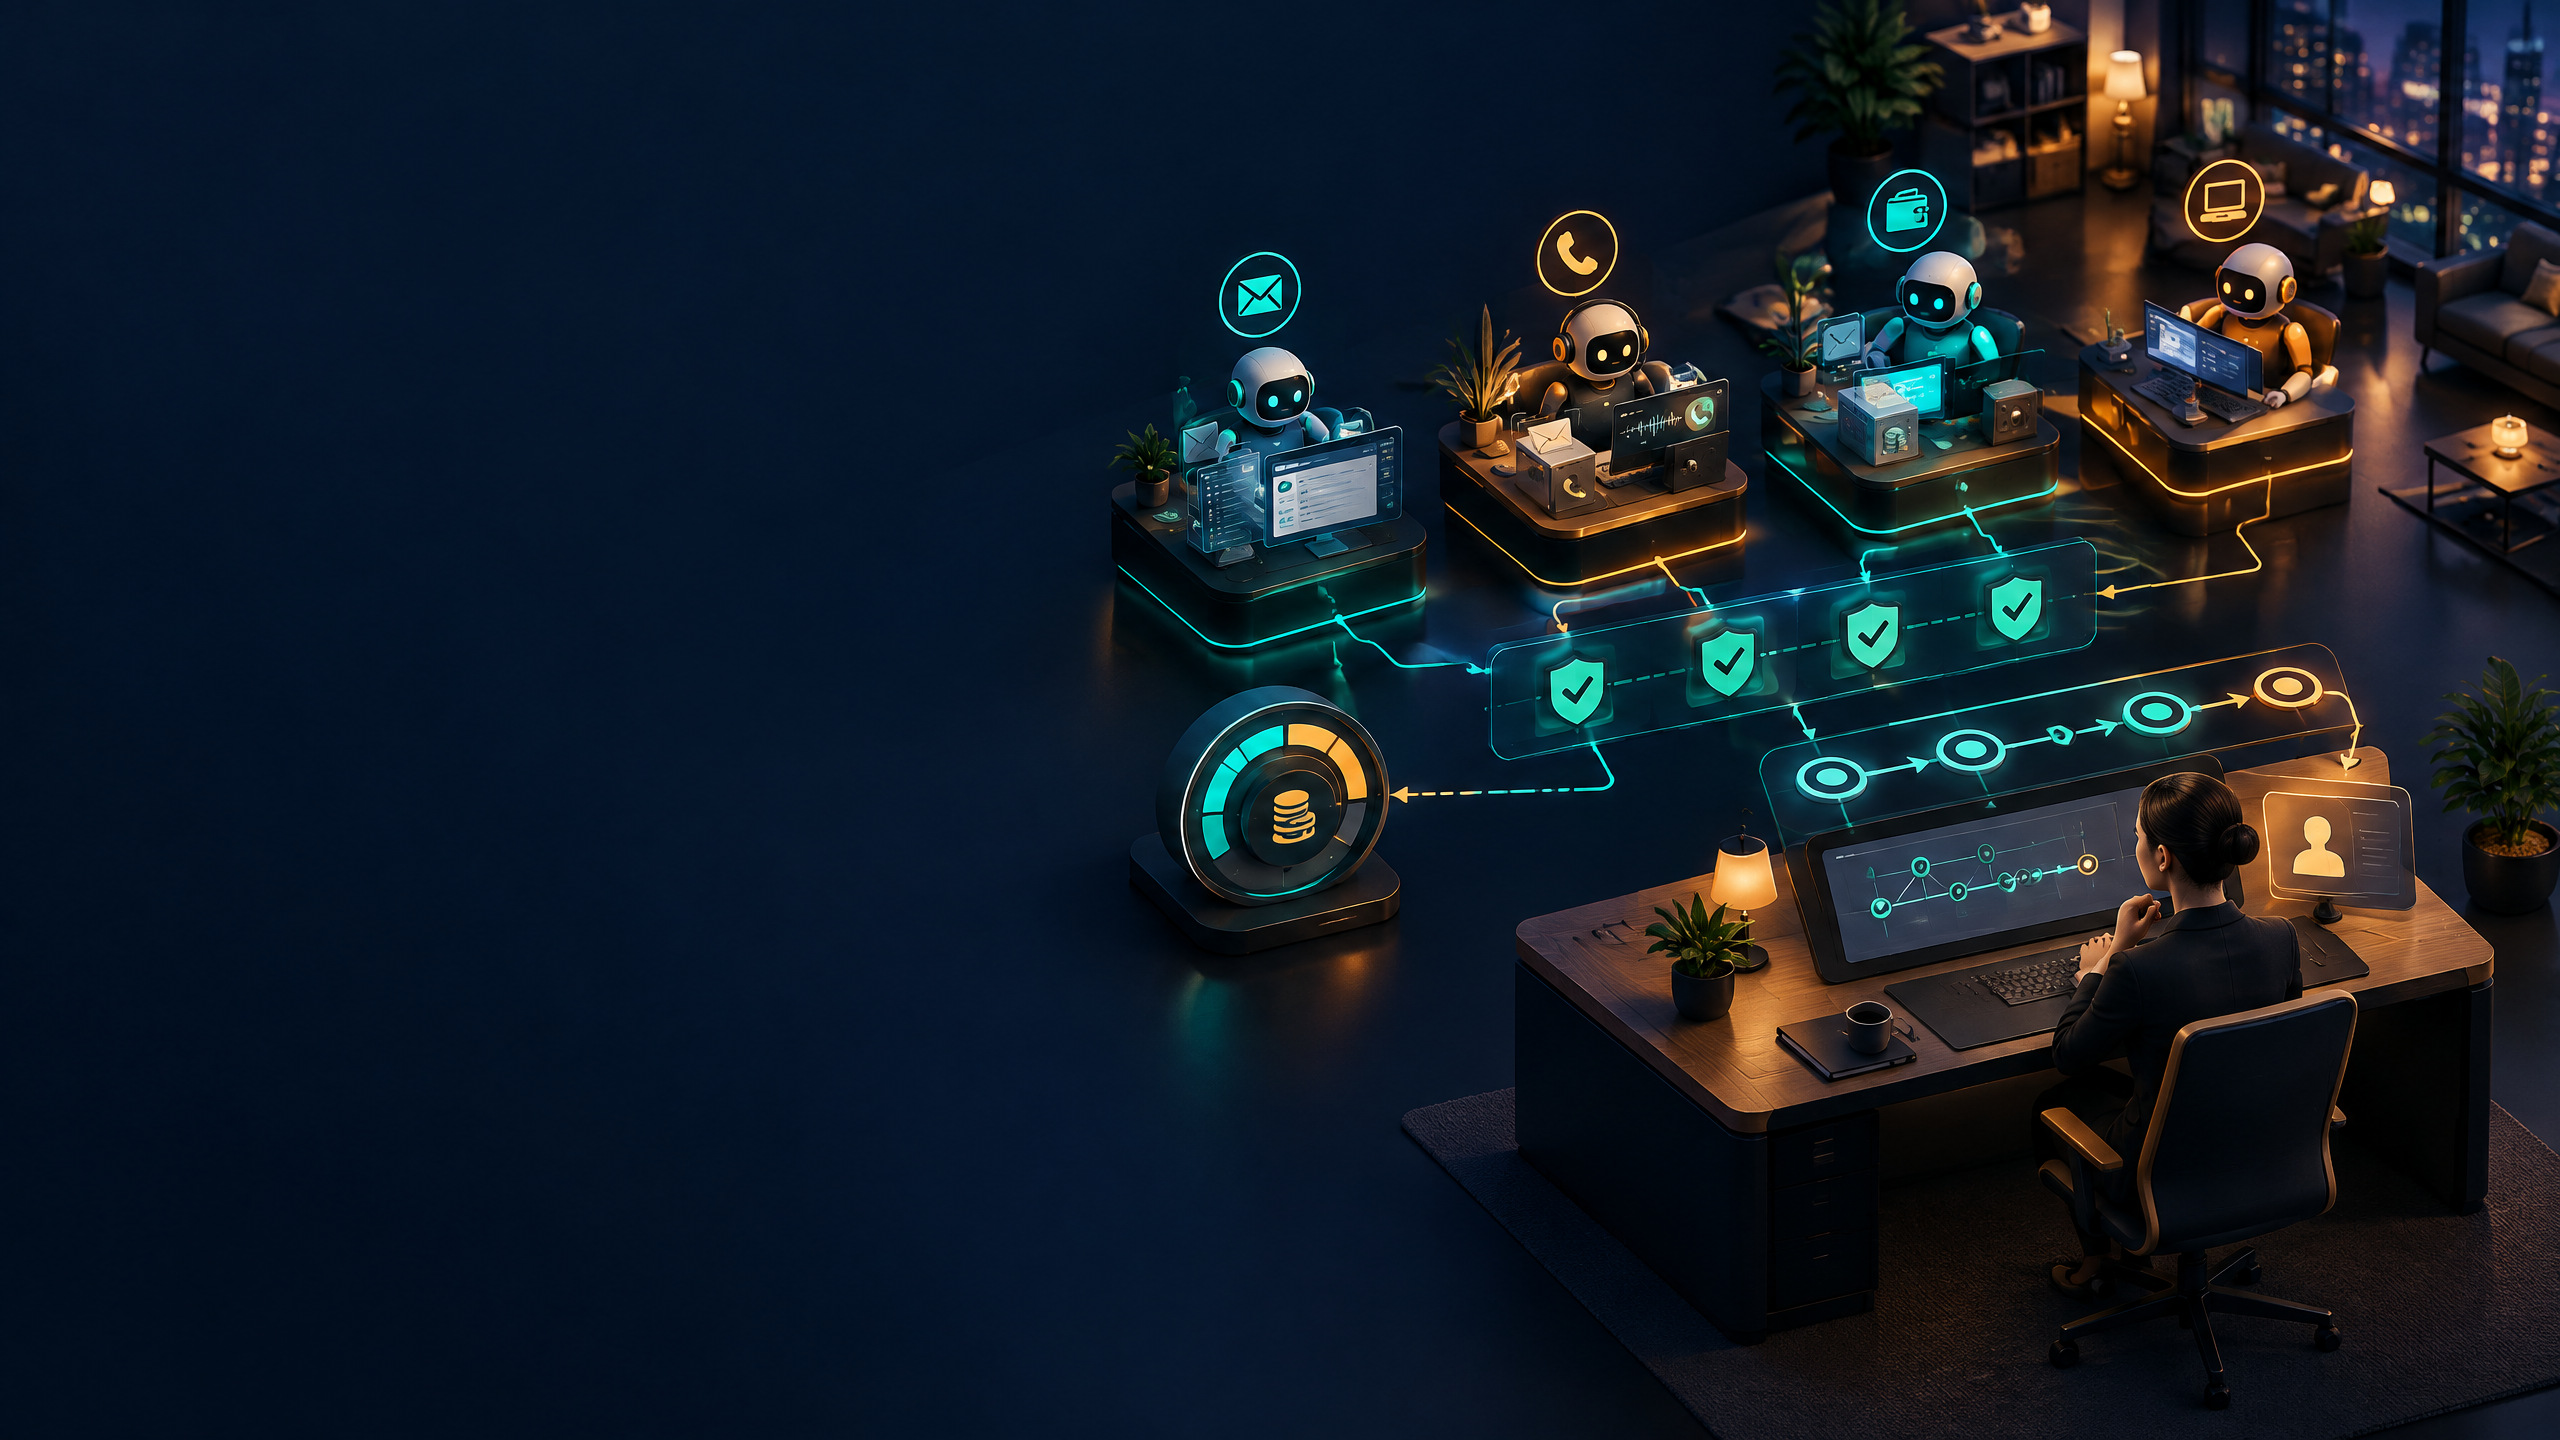
That becomes less defensible when an agent is persistent, conversational and able to act across several systems. The market examples are visible in consumer products. TechCrunch reported that Instinct began rolling out a dedicated assistant email address in September, allowing the agent to create or manage accounts, contact businesses and follow up on requests without using the user’s personal inbox. The same 3 October overview described Wajo’s Fo as having its own email address, phone number and payment card.
Those are company and product examples, not a standard for enterprise deployment. They do illustrate the underlying architecture: a system needs a recognisable way to receive messages, authenticate to a service and leave a trace of what it did. The moment that identity can contact a customer, sign into a service or initiate a purchase-related step, the questions move from novelty to governance.
Separate identity, authority and accountability
A useful operating model has three layers. They should be related, but they should not be treated as interchangeable.
| Layer | The question it answers | Example evidence | What can go wrong if it is missing |
|---|---|---|---|
| Operational identity | Which agent or service account acted? | Unique ID, authenticated address, workload identity | Actions disappear into a shared human login |
| Delegated authority | What was this agent permitted to read, propose, change or commit to? | Scope, tool allowlist, limit, approval threshold | A valid identity is mistaken for unlimited permission |
| Accountability | Which human or business owner is answerable for the outcome? | Named owner, escalation route, incident record | A failure is bounced between vendor, team and operator |
A dedicated inbox can help with the first layer. It does not solve the other two. A calendar agent may legitimately read availability and propose times, for example, while still needing a human decision before it accepts a contractual meeting, discloses a customer detail or sends a message in a senior executive’s name.
This is why an agent should not simply inherit “whatever access the employee has.” Employees have varied responsibilities, judgment and accountability routes. An agent needs a written purpose and a smaller, reviewable set of permissions.
The seven-field agent delegation record
Before an agent is allowed to act in a marketing, sales or service workflow, create one short record that a non-technical leader can read. It does not need to be a burdensome policy document. It needs to be specific enough that operations, security and commercial owners can make the same decision.
- Identity: a stable name or service identity that appears in logs and external communication where appropriate.
- Business owner: the accountable internal role, not merely the person who configured the prompt.
- Purpose: a bounded job such as research preparation, meeting coordination, campaign QA or customer-service triage.
- Data and tool scope: systems, datasets and tools the agent may use, with exclusions stated clearly.
- Action boundary: what it can read, draft, propose, send, change, purchase or publish.
- Approval and exception rule: which actions need a human confirmation, and when the agent must stop rather than guess.
- Revocation and evidence: how access is removed, where the action record lives and who reviews a material exception.
This record is useful whether the agent is a vendor product, a custom workflow or a collection of tools. It prevents a vague instruction such as “help with customer follow-up” from becoming an accidental mandate to contact anyone in the CRM, use every available data field or send an unreviewed offer.
A marketing example: from research assistant to external representative
Consider an account-based marketing workflow. An agent may assemble public company information, identify potential stakeholders and prepare a source-linked account brief. That is a research task. It can be useful with read-only access to approved public sources and a defined format.
The next step is different. If the same agent updates a CRM, scores an account or drafts a message, it now touches internal commercial data. It needs separate permissions and an audit trail. If it sends an email externally, it becomes a representative of the business. The identity shown to the recipient, the approved claims, the contact policy and the human escalation route now matter.
A sound workflow does not pretend those are all the same task. It gives the agent authority in stages:
| Stage | Useful agent role | Default boundary | Human decision |
|---|---|---|---|
| Research | Find and summarize approved sources | No access to private records | Validate material claims before use |
| Preparation | Draft a brief or message | No automatic send or system-of-record update | Approve audience, claim and tone |
| Internal action | Create a proposed CRM update or task | Write only to a review queue | Accept, edit or reject record changes |
| External action | Send a defined follow-up or request | Approved template, recipient and stop rules | Approve new categories, sensitive cases and commitments |
That is governed delegation, not bureaucracy. It lets a team increase the volume of safe preparatory work without giving every new capability the authority of a commercial director.
Why shared human credentials are a poor long-term answer
Using a named employee’s credentials can look convenient at the start. It also creates ambiguity: did the employee act, did the agent act, or did another tool use the session? It complicates access review, makes it difficult to remove a single agent’s authority and weakens the evidence needed after an error.
Microsoft’s 2026 Digital Defense Report frames the wider security issue clearly. Microsoft says securing agents involves their identities, permissions, data and tools, alongside traditional foundations such as authorization, least privilege, monitoring and testing. The report also identifies agent identity, appropriate access, authentication between agents, attribution and the ability to revoke access as areas organizations need to consider.
The implication is not that every agent needs to be treated as a legal employee. It is that every agent that can affect a system should have an operational record at least as clear as the service account it uses.
A 30-day starting point for commercial teams
Start with a small inventory rather than a large transformation program.
Week 1: list the agents that already touch work. Include chat-based assistants, CRM automations, browser agents, third-party plugins and scheduled workflows. Record the owner and the task they are meant to perform.
Week 2: separate observation from action. Mark which agents can only read or summarize, which can draft, which can update an internal system and which can interact with people or payments.
Week 3: create the first delegation records. Use the seven fields above for the agents with the highest commercial, privacy or reputational consequence.
Week 4: test revocation and escalation. Confirm that the business can disable an agent, identify its recent actions and route a non-standard case to a named person. If it cannot, the deployment is not yet as controllable as the commercial promise suggests.
This is where AI governance and Gemini Enterprise agentic AI should meet: a useful workflow, evidence of the boundary and an accountable operating owner. For a separate look at what happens when an agent moves from answer to action, see our analysis of Cue by Manus and personal agent-team governance and agent liability in commerce.
What this does not establish
The current market examples do not establish that dedicated agent identities are safe in every context, that a personal-agent feature meets an enterprise security standard or that a particular product should be used for regulated workflows. Nor do they prove that an agent’s email address reflects the real identity of a customer behind it.
They do make one operating question harder to avoid: as agents become more persistent and capable, organizations need a way to distinguish the technical identity that acted from the authority that was granted and the person who remains responsible.
For leadership reading, Competing in the Age of AI is an optional Amazon UK Associates resource on operating-model change. It is not evidence for the capabilities, security or commercial outcomes of any named agent product. Integrated.Social may earn from qualifying purchases.
The bottom line
An agent with an email address, a phone number or a payment method is not automatically a trusted actor. Those capabilities simply make the need for governance more visible. Give each agent a durable operational identity, a narrow authority record, a human owner and a real stop path. Then delegation can become more useful without becoming untraceable.
References
- TechCrunch: All the AI agents that can live in your text messages, 3 October 2026.
- TechCrunch: Viral AI assistant Instinct now has its own email address, 9 September 2026.
- Microsoft: Insights from the 2026 Microsoft Digital Defense Report, 1 October 2026.
About the Author
Modi Elnadi is the founder of Integrated.Social, a London AI growth consultancy working across B2B, B2C, B2B2C and DTC. Since 2014, he has helped commercial teams connect performance marketing, AI-search visibility and governed AI workflows to clear evidence and accountable outcomes. His view: delegation earns trust only when its identity, authority, evidence and human escalation path are visible. Connect with Modi on LinkedIn or explore AI governance.